
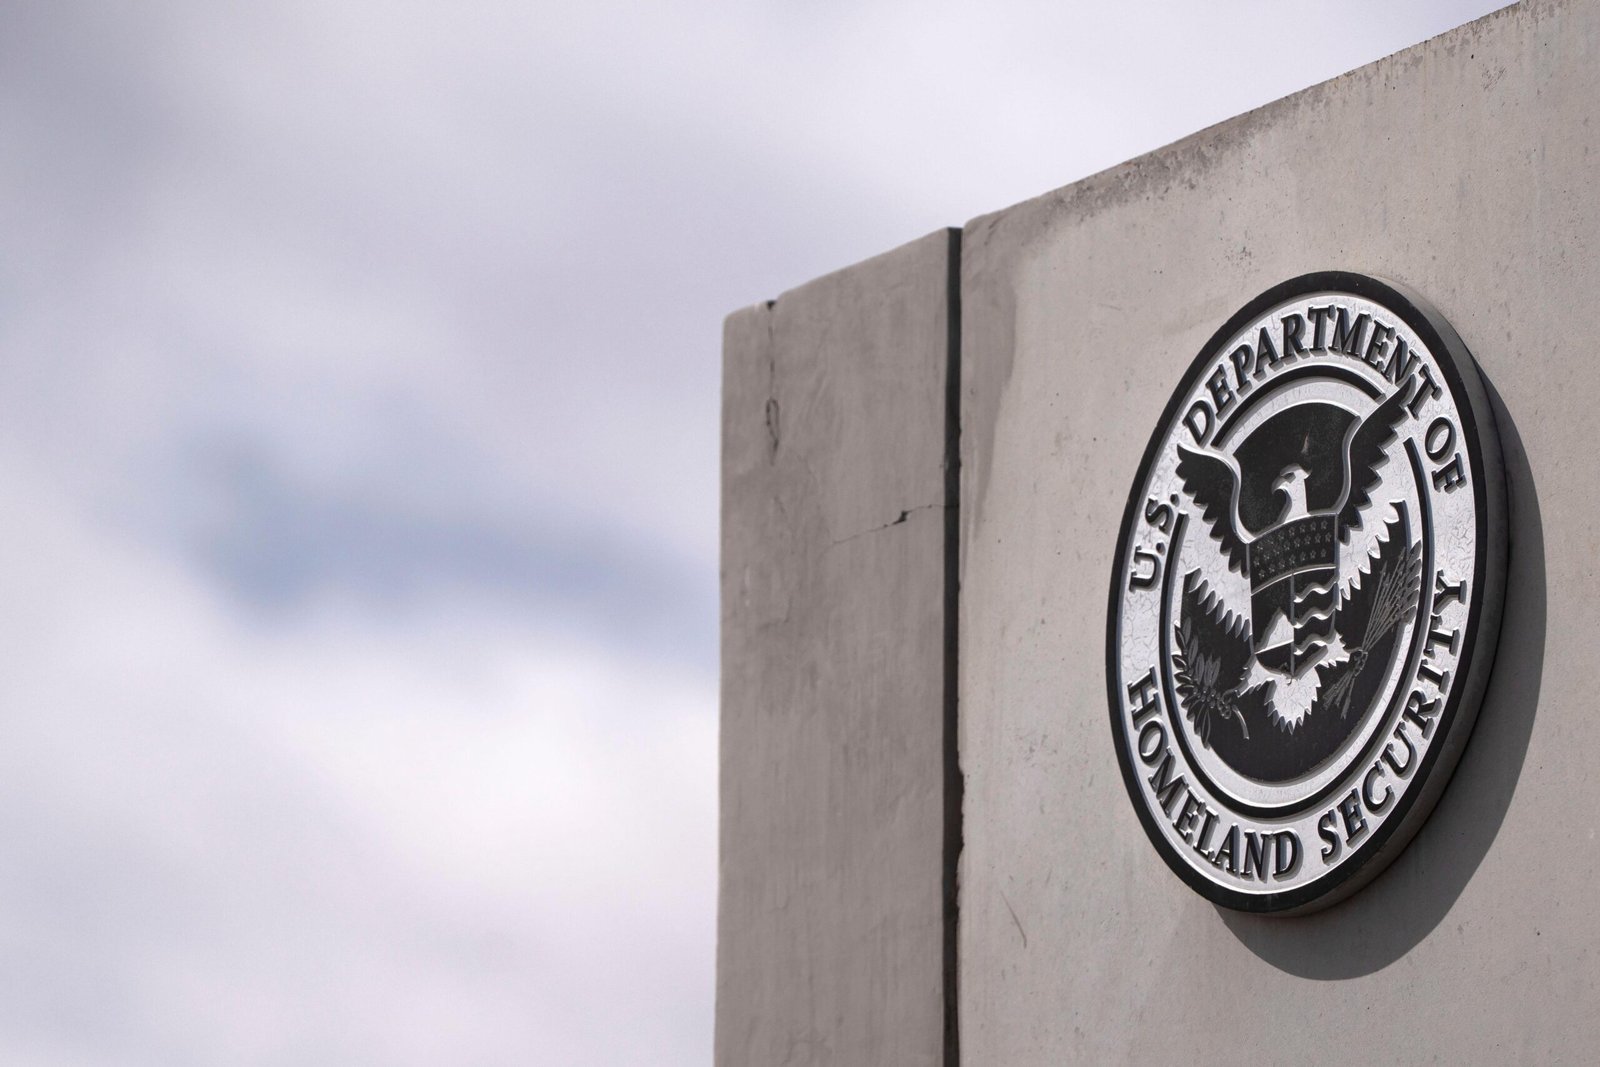
A hacker has stolen personal data on more than 41,000 US Department of Homeland Security employees. Names, job titles, phone numbers, email addresses, and office locations were all exposed.
The breach hit staff at Immigration and Customs Enforcement and Customs and Border Protection. Records from the Cybersecurity and Infrastructure Security Agency, US Citizenship and Immigration Services, and Homeland Security Investigations were also included. TechCrunch and Wired first reported the leak.
How the data was taken
The hacker, who uses the name “Department of Peace,” got in through Okta. Okta is an identity and access management service that DHS uses to control employee logins. About 21,000 records belong to CBP staff. Nearly 7,000 belong to ICE employees.
Okta sits at the centre of this story. One compromised identity provider gave an attacker a wide view of an agency that spans several departments. That single access layer carried a lot of weight.
Why the leak matters
DHS has tried to keep the identities of CBP and ICE agents private. Those agents have carried out immigration raids across the US. The agency has also tracked down people who criticise it online. A list of names, offices, and phone numbers undercuts that secrecy.
“They have our information, so it’s only fair that we have theirs,” the hacker told TechCrunch.
The leaked files also reportedly show which DHS teams can reach surveillance tools, including facial recognition systems. That is a bigger problem than a contact list. It maps who inside the agency can watch people, and with what.
This is the second major US government leak in weeks. Hackers recently stole data on FBI employees and job applicants. Private firms are leaking too, as the cyber-attack on the owner of Phase Eight and Hobbs showed this month.
Where the data went
The information was reportedly passed to security researcher maia arson crimew. She shared it with Distributed Denial of Secrets, a nonprofit that hosts leaked datasets. The group is now publishing the files under the name “Icepick.”
Researchers are still working through the trove. DHS has not said whether it has notified affected staff. The agency has also not confirmed how long the intruder had access.
For federal employees, the practical advice is familiar. Watch for phishing that quotes your real job title or office. Attackers use exactly this kind of detail to make a fake message look internal, which is the same pattern seen in the Belgian e-signing hack.
The Verge reported the breach on October 28, citing TechCrunch and Wired.
The Netherlands, for internationals
One email a week: the week's news for internationals in the Netherlands, new practical guides and what changed in the cities. No spam, unsubscribe any time.