
Google says one of its Android manufacturing partners hid a backdoor inside 1.3 million devices. The company has now dismantled the backdoor and ended the relationship.
The partner was Videostrong Technology, based in Shenzhen, China. Google banned the firm from building or selling certified Android devices. It also barred Videostrong from supplying software for them.
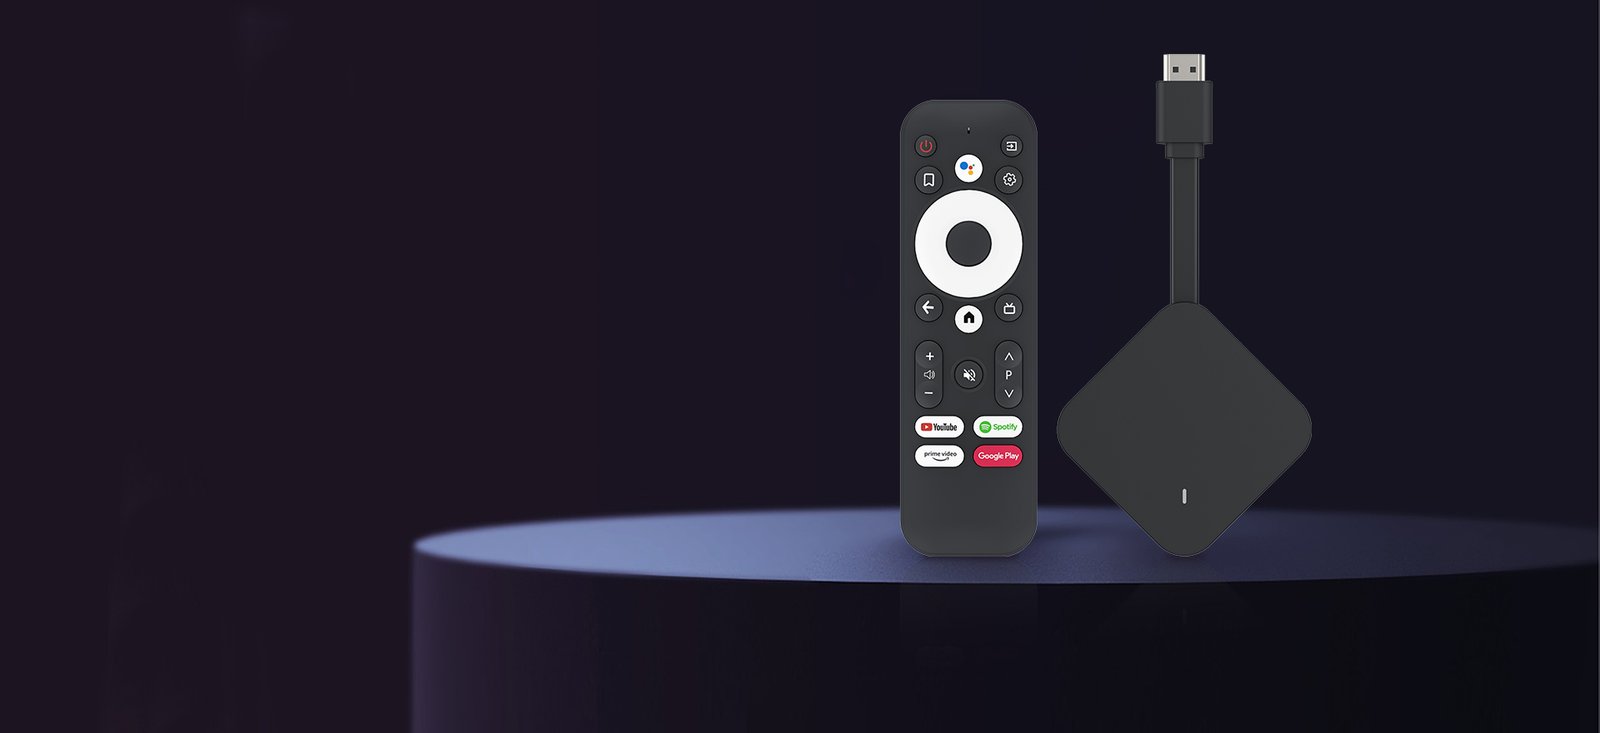
The affected hardware was mostly Android TV set-top boxes. The malware shipped inside many models and brands over several years. Google says it also reached telehealth devices, karaoke machines, and digital signage units.
Videostrong used obfuscation to load the payload after a device booted for the first time. Owners had no idea their hardware was being used for someone else’s business.
The devices were quietly drafted into ad fraud, data exfiltration, and unauthorized network traffic. Google says the operation existed for money, not research or testing.
“Videostrong monetized the backdoor by selling access to criminal affiliates,” Google said in its statement. Those affiliates then loaded their own modules onto infected devices.
Some modules enrolled devices into residential proxy networks. Others pushed more malware onto machines that were already compromised. Each affiliate ran its own supply chain, which made the network harder to map.
Google also took down the command-and-control domains behind the affiliate modules. It estimates that move cut off access to at least 10 million more compromised devices. Those affiliates used other distribution channels as well, so the full reach is unclear.
The company says it has changed its review process for device manufacturers. It did not say how long the backdoor had been active or how many device models carried it.
The practical lesson for buyers is uncomfortable. A certification badge proves that a device passed a review at some point. It does not prove that the firmware stays clean forever. Cheap streaming boxes are a known weak point, because update support often ends early. Earlier this year, abandoned Popcorn Time updaters were disabled before they could build a similar zombie army, which mylistingo covered here.
The incident also puts pressure on Google’s partner program. Android’s openness is a selling point for manufacturers. That same openness gives Google little visibility into what partners install after certification.
Google has not published a full list of affected brands. Owners of budget Android TV hardware should watch for firmware updates from their seller.
Source: The Verge
The Netherlands, for internationals
One email a week: the week's news for internationals in the Netherlands, new practical guides and what changed in the cities. No spam, unsubscribe any time.